Secure Your Organization with a Proven Acceptable Use Policy Template
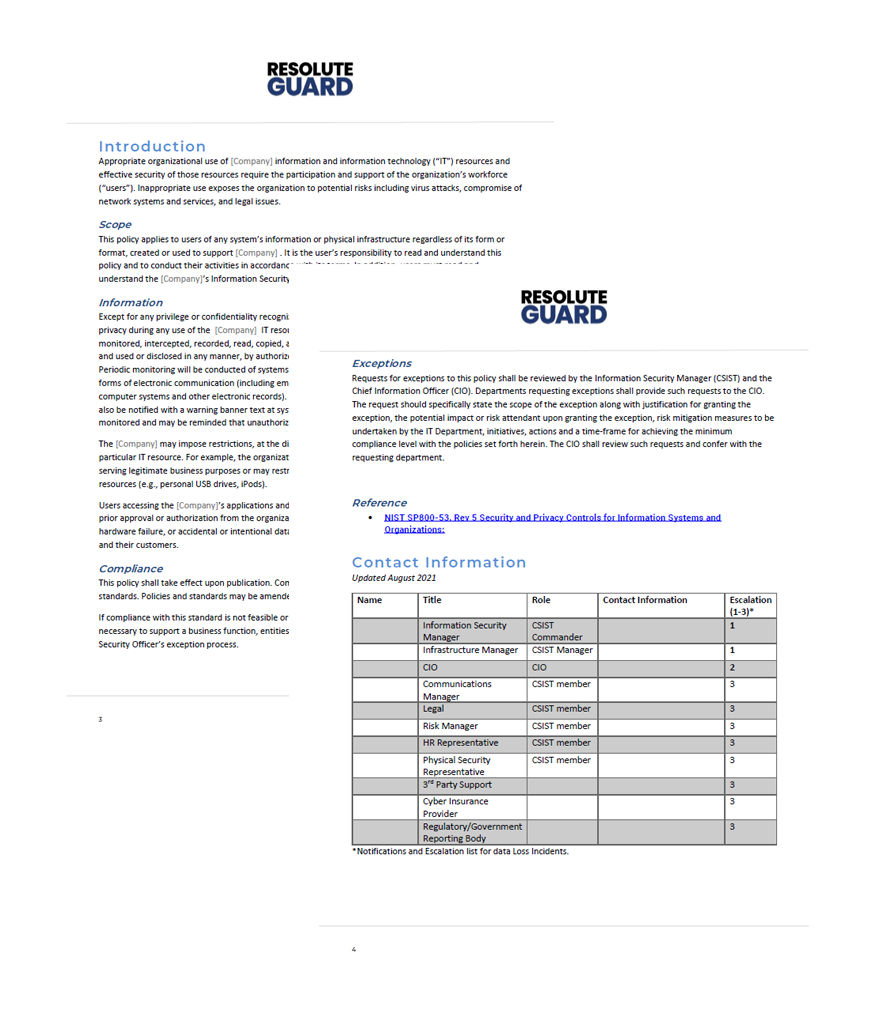
Protecting your organization’s IT resources is more critical than ever. Inappropriate use of technology not only exposes you to cyber threats but also creates legal and compliance risks. That’s why we’ve created a comprehensive Acceptable Use Policy (AUP) Template, aligned with NIST CSF ID.AM-1 standards, to help you safeguard your systems and data.
What’s Inside the Template:
✅ Clear Roles & Responsibilities — defines accountability from CIOs to IT staff.
✅ Acceptable vs. Unacceptable Use — outlines what’s permitted, restricted, and prohibited.
✅ User Accountability & Equipment Management — ensures proper care and reporting for IT assets.
✅ Social Media & Off-Site Use Guidelines — reduces risk from personal devices and online activity.
✅ Exception Logging Framework — enables structured tracking of approved exceptions.
✅ Reference Materials & Compliance Guidance — based on NIST SP800-53 Rev 5 and CIS best practices
Why Download This Template?
✔ Save time creating a policy from scratch
✔ Ensure alignment with industry-standard cybersecurity frameworks
✔ Reduce risks of data loss, non-compliance, and insider threats
✔ Provide employees with a clear, enforceable guide to using IT responsibly
👉 Download your free Acceptable Use Policy Template today and take a critical step toward stronger cybersecurity and compliance.